Brightpick Vulnerability Disclosure Policy
Brightpick is open to reports from security researchers and the public. If you believe you have found a security vulnerability in a Brightpick product or service, please report it to security@brightpick.ai (PGP key available in our security.txt).
In scope
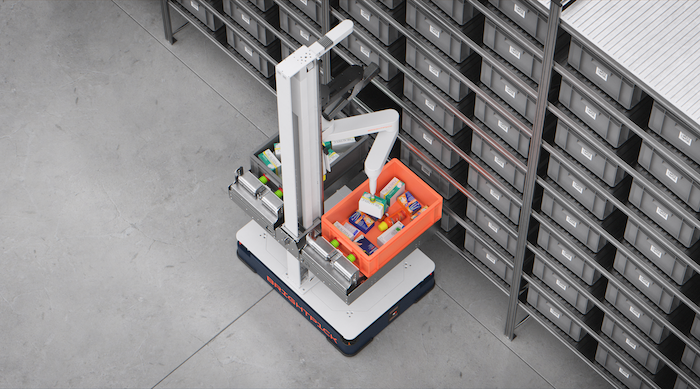
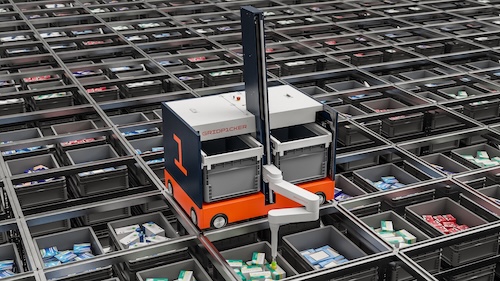
- Brightpick products with digital elements: Brightpick Autopicker, Brightpick Gridpicker, Brightpick Intuition and Brightpick Analytics, including the cloud components required for their operation.
- Production web services at brightpick.ai and its subdomains (*.brightpick.ai), including customer-facing dashboards and authentication endpoints, and the public APIs of those services.
- Mobile and web client applications officially distributed by Brightpick.
- Any other production system operated by Brightpick that is reachable from the public internet, including remote-access and monitoring gateways. Any demonstrable security impact on a live Brightpick production asset qualifies, regardless of how the asset was discovered or whether it appears in this list.
Out of scope
- Customer deployments and customer data — the security of customer installations is governed by the applicable customer contracts.
- Production robot fleets at customer sites — never test against a deployed fleet or a live warehouse.
- Third-party services that Brightpick does not operate.
- Internal Brightpick systems that are not reachable from the internet.
Testing Brightpick Intuition is possible exclusively in a dedicated Brightpick test environment, by prior arrangement and under agreed Rules of Engagement — contact security@brightpick.ai.
Qualifying vulnerabilities are findings with a demonstrable impact on business logic, on the confidentiality of customer or operational data, or on the safety and integrity of warehouse automation.
Findings we do not normally treat as vulnerabilities (unless a concrete security impact is demonstrated): issues requiring root/jailbreak, malware or full local compromise of the user’s device; output of automated scanners without a proof of concept; missing HTTP security headers or SPF/DMARC configuration without demonstrable abuse; self-XSS, clickjacking on pages without sensitive state-changing actions, tab-nabbing; denial-of-service and volumetric findings.
In your report, include the affected product or URL, a description of the issue, steps to reproduce, and your assessment of the impact.
Reporting through the national coordinator. If you prefer not to contact us directly, you may report the vulnerability to the national coordinator for vulnerability disclosure in Slovakia, the National Cyber Security Centre SK-CERT (NBÚ), at incident@nbu.gov.sk. SK-CERT will forward the report to us, preserve your anonymity and can independently verify the finding. We cooperate fully with SK-CERT in coordinated disclosure.
Our commitments. We will acknowledge your report within 7 business days, give you a validation decision within 14 working days, and keep you informed at least every 30 days while the issue is open. We ask that you give us up to 90 days to remediate before public disclosure; we are happy to agree on a different timeline where appropriate.
Rules. Do not access or modify customer data, do not degrade production or warehouse operations, no denial-of-service testing, no social engineering or physical attacks, and never attempt to influence the behaviour of deployed robots — human safety comes first. We will not pursue legal action against research conducted in good faith within these rules, and we will gladly credit you in our advisory if you wish.
Recognition. Reports submitted through this channel are not automatically rewarded. Monetary rewards are handled separately under Brightpick’s internal bug bounty programme, which is not open to the public and operates on an invitation basis.
Security updates and product support
Brightpick provides security updates for its products throughout their support period, free of charge and through secure distribution channels, without undue delay once a vulnerability has been remediated. Information on the support period, the update mechanism and the recommended secure configuration of each product is provided in the product documentation. Customers with questions about the security of their installation should contact their Brightpick support representative or security@brightpick.ai.
Questions
For anything not covered here — scope questions, a request for Rules of Engagement, or a press or customer enquiry about a published advisory — write to security@brightpick.ai.